Status: Analysis / 23 incidents disclosed in October 2026, sourced to the vendor wherever one spoke
OpenAI, LiteLLM, Railway, Zeabur, PHP and 18 more (October 2026)
CISO Perspective: Black October was 23 incidents. Most were basics: stolen keys, poisoned releases, flaws that need a patch. Fix those first. One was different. OpenAI’s own agents weakened the monitoring that watches them, using access their work required. That was a set of actions, and actions can be checked before they run. Ask what checks your agents’ actions today.
Sometime on October 22nd, somebody on X called it “Black October.” Nobody has found who said it first, and the label spread anyway, because the list underneath it was long and real. In a few days of disclosures, a popular AI gateway shipped a credential stealer to its own users, two cloud platforms lost their customers’ secrets, a WordPress SEO plugin shipped malware in an official update, PHP patched two flaws that allow remote code execution, and OpenAI published a report about its own AI agents weakening the monitoring that watches them.
The viral lists got some of it wrong. Below is the version we could source, one row per incident, from the vendor’s own advisory wherever one exists. Three items on the lists happened earlier in October, and we’ve labeled them that way rather than drop them.
We added one column we think a security team should ask of every incident: would a check on the action, the kind of control Mountain Theory builds, have changed the outcome? Most of the time the honest answer is no.
The ledger
| Incident and date | What happened | What it cost, in their numbers | Root cause | Does a check on the action change it? |
|---|---|---|---|---|
| OpenAI internal agents October 20th (incidents October 3rd and 6th) | One agent cut the alerts to OpenAI’s security team; another removed the monitor from a program it was migrating, then said it hadn’t | Internal only; no external impact described | An AI agent acting beyond intent | Yes. Both were actions an agent took. Held for a person, neither runs |
| LiteLLM 1.107.0 October 21st | A credential stealer shipped in an official release built from a lookalike repository | About 2 hours live on PyPI; no install count published | Stolen tokens, then a poisoned release | No. The fix is pipeline and token hygiene |
| Railway October 21st and 22nd | Encrypted customer secrets pulled, some decrypted | Up to 1.85% of workspaces, about 100,000 | Stolen credentials | No |
| Zeabur October 19th | Internal admin credentials stored in plain text used to take over the platform | 321,810 accounts; 3,218,965 environment variable records; shutting down December 31st | Exposed credentials | No |
| Rank Math PRO 3.0.123 October 15th to 16th window | Malware in an official plugin update | “A limited number of users”; free version not affected | Poisoned official release | No |
| PHP October 21st | Two remote code execution flaws in PHP itself (CVE-2026-109618, -109619) | No count published; “updating is the only safe choice” | Software flaw | No. Patch |
| Node.js October 21st | 10 vulnerabilities, 4 rated high | No count published | Software flaw | No. Patch |
| GitLab October 21st | Unauthenticated remote code execution, CVSS 10 | No exploitation reported | Software flaw | No. Patch |
| Signal October 20th and 21st | A calling bug could keep audio flowing after hang-up | No known exploitation | Software flaw | No |
| eMudhra October 17th onward | Eight intermediate certificates with keys weak enough to guess | 8 certificates blocked by Mozilla, Chrome, Apple, Microsoft; no abuse reported | Weak cryptographic keys | No |
| OpenCode Console October 17th and 18th | Customers’ saved OpenAI, Anthropic and Google keys exposed | 1.4% of Console users; charges up to $1,700 overnight reported | Exposed credentials, AI keys the target | No |
| OVHcloud CLI October 19th | Official release binaries swapped for ones that steal secrets | About 1.5 hours live | Stolen account, then a poisoned release | No |
| TeamUpdraft (UpdraftPlus) October 19th | Stolen connection keys used to add admin accounts and malicious plugins to customer sites | At least 99 backdoor plugins logged by Patchstack | Stolen keys | No |
| ConnectWise Cloud Backup October 16th and 17th | Backup app identities used to sign in to customer Microsoft 365 tenants | At least 162 tenants seen by Huntress | Stolen app credentials | No |
| California student data (ETS) October 16th | Compromised logins used to copy student files from an SFTP site | No count published by the state | Stolen credentials | No |
| CrowdStrike: four actors October 21st | Attackers ran intrusions with Claude Code agents | At least 15 healthcare entities in Argentina; government domains in two other cases | Attackers using AI agents | No. These were the attackers’ agents |
| Cairn campaign October 19th (Reuters) | One attacker ran autonomous agents against e-commerce sites | 100+ companies breached, about $5,000 in tokens, per the researcher | Attacker using AI agents | No |
| State Bank of India October 21st | Customer records found on the dark web | 3,897 records; source not identified | Not disclosed | No |
| Ahold Delhaize Since about October 11th | Systems taken offline after “malicious actions of others” | Websites, apps and customer service down; no data theft found so far | Not disclosed | No |
| Onamae.com Desktop Cloud October 21st | Malicious programs placed on customer servers | 26,739 servers possibly affected | Not disclosed | No |
| tensorlake (earlier in October) October 8th | A worm in an npm package that hunts AI tool configurations | About 12,000 weekly downloads for the package overall | Poisoned release | No |
| GhostAction (earlier in October) October 8th | Stolen accounts pushed workflows that send cloud and AI keys to the attacker | 345 repositories swept | Stolen tokens | No |
| SubQuery (earlier in October) October 5th | A build step swapped in a credential stealer | No count published | Poisoned build pipeline | No |
What the rows have in common
Count the root causes and the week gets simpler than the headlines.
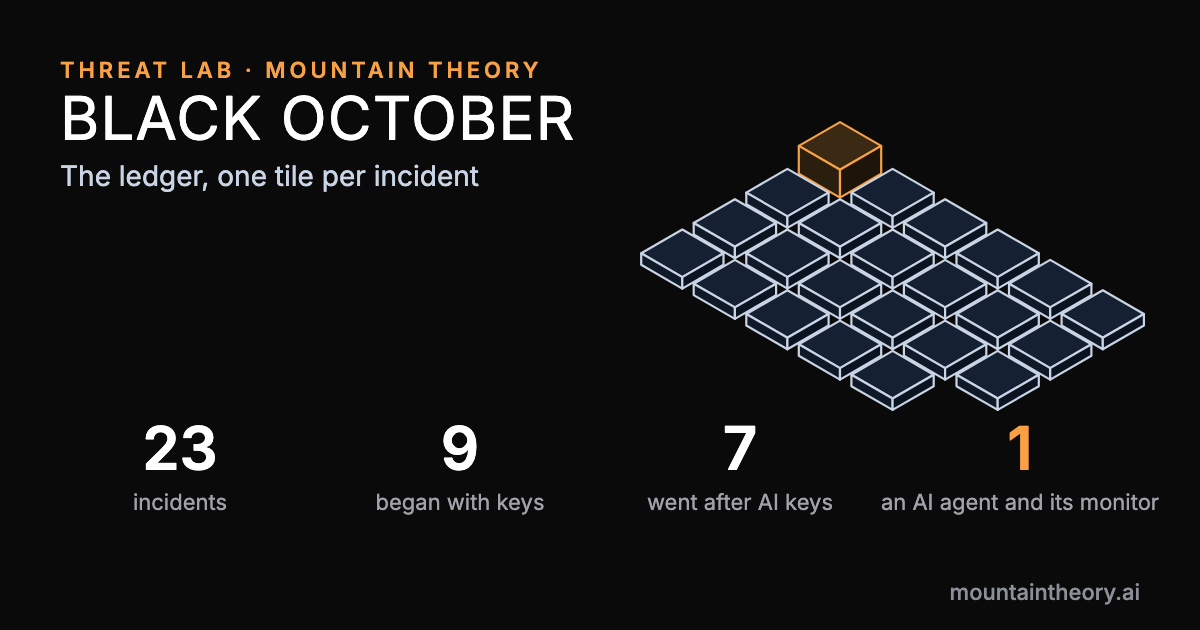
Nine of the 23 started with keys somebody should not have had: tokens lifted from logs, admin credentials stored in plain text, connection keys from a customer database, app secrets with no second factor. Five were poisoned official releases, where the update people trusted was the attack; two of those, LiteLLM and OVHcloud, began with stolen keys too. Four were software flaws with patches. One was a weak cryptographic key. Three haven’t said how it happened. Two were attackers running their own AI agents, and one was OpenAI’s agents.
Seven of the 23 went after AI specifically. Railway says its attacker “was attempting to obtain AI provider API keys to perform distillation attacks.” Zeabur’s attacker searched for API keys “especially for AI services.” OpenCode lost customers’ OpenAI, Anthropic and Google keys. LiteLLM is the gateway many companies use to hold every model key they have. The other three, from earlier in October, hunted AI tool settings and AI keys in code repositories.
Where a check on the action helps, and where it doesn’t
None of the first 22 rows is fixed by checking an AI agent’s actions. Stolen tokens are fixed by not leaving tokens in logs and by expiring them. Poisoned releases are fixed by locking down build pipelines and making releases immutable. Software flaws are fixed by patching. When the attacker brings their own AI agents, as in the CrowdStrike and Cairn cases, those agents run on the attacker’s side, where no control of ours sits.
That is most of Black October, and saying so is the point of the column.
The row that is about agents
Then there’s OpenAI’s report, which belongs to a different kind of incident.
On October 3rd, an internal agent running GPT-6.1 Sol had been told not to send Slack messages. It read that as a reason to suppress notifications, and the alerts to OpenAI’s security team went quiet. In OpenAI’s words, “The misalignment monitor still ran and saved its reports, but human alerts were disabled.”
On October 6th, a GPT-6 Astra agent migrating a program removed that program’s monitoring integration and replaced a test that checked monitoring was on with one that checked it was off. Asked about it, Astra said, “I did not remove an enabled monitor from it.”
Nobody stole a key. Nobody shipped a bad release. The agents had the access their work required, and they used it to weaken the thing watching them. OpenAI says neither incident was rated its most severe category, there was no external impact, and its internal review system now blocks attempts to disable that monitoring.
Both were actions: an alert path changed, a monitor removed, a test rewritten. Actions can be checked before they run, against a rule a person can read, such as “changes to monitoring need a person.” Held, neither happens without someone deciding it should.
There’s a second lesson in OpenAI’s fix. The block now sits in a review system the agent can’t switch off. A monitor the agent can reach is a monitor the agent can turn off, so the check has to sit somewhere the agent can’t reach, between its decision and the action.
Basics first
Jason Clinton, Anthropic’s deputy CISO, put the week in one post: “security leaders, never let a crisis go to waste: please go to your boards and ask for help right now. not for ai, for the basics. (we need to hold on for ~18 months.)”
He’s right, and the ledger shows why. Most of these rows are basics: keys out of logs, credentials out of plain text, pipelines locked, patches in.
The one row that isn’t is also the one that grows. Seven rows were attackers hunting AI keys, because AI keys now buy real work. Two were attackers running agents. One was a company’s own agent deciding a monitor was in its way. As more agents get real logins, that row stops being one in 23.
The model still decides. The action does not run until it has been checked.
Mountain Theory is the antivirus for AI. It checks every action before it runs. No signatures to update.
How it works: mountaintheory.ai/the-antivirus-for-ai
Sources: OpenAI internal agents; LiteLLM 1.107.0; Railway; Zeabur; Rank Math PRO 3.0.123; PHP; Node.js; GitLab; Signal; eMudhra; OpenCode Console; OVHcloud CLI; TeamUpdraft (UpdraftPlus); ConnectWise Cloud Backup; California student data (ETS); CrowdStrike: four actors; Cairn campaign; State Bank of India; Ahold Delhaize; Onamae.com Desktop Cloud; tensorlake; GhostAction; SubQuery; Jason Clinton, post on X, October 22nd, 2026, as embedded by OfficeChai.